Cyber Threat Intelligence Courses & Training Insights
In-depth guides on threat intelligence, OSINT, HUMINT, information security, and more. Written by practitioners, designed to accelerate your cybersecurity career.
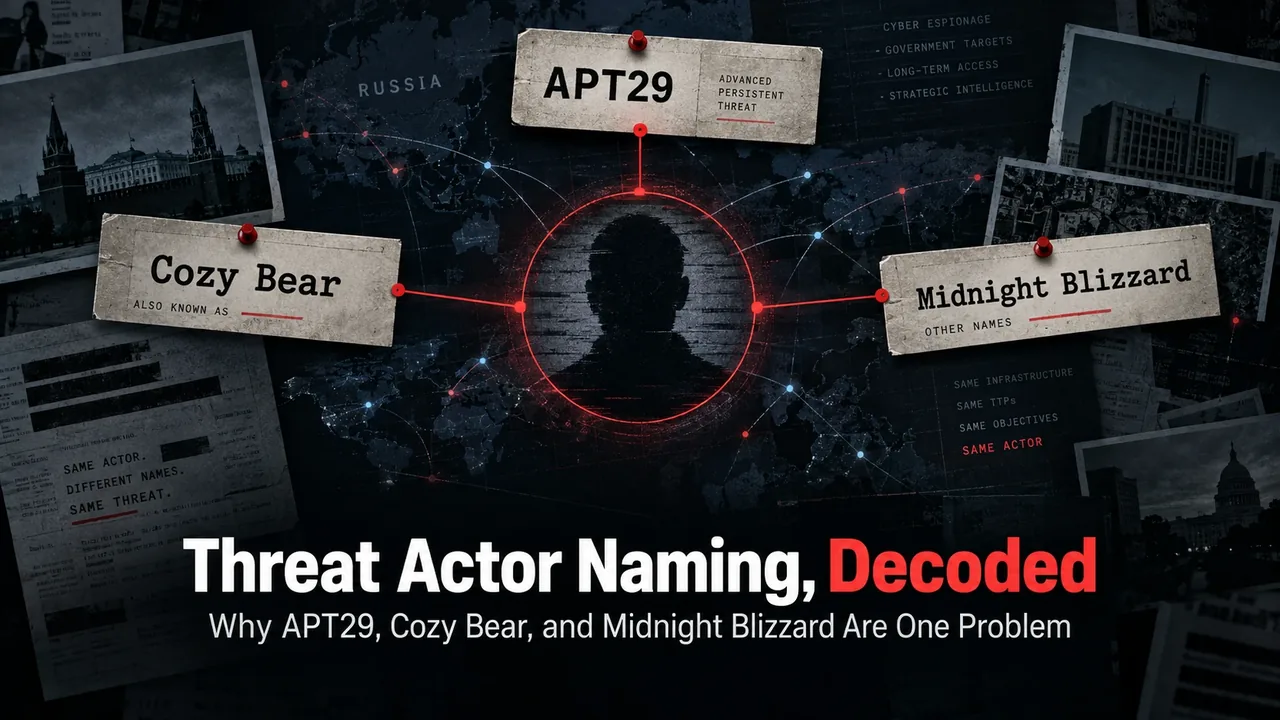
Threat Actor Naming, Decoded: Why APT29, Cozy Bear, and Midnight Blizzard Are One Problem
In July 2026 Google renamed its entire catalogue, and APT29 became ICE RELIC. It already answered to Cozy Bear, Midnight Blizzard, UNC2452 and two dozen more. Here is what each vendor's naming scheme actually encodes, and why treating an alias as an equals sign will eventually burn you.
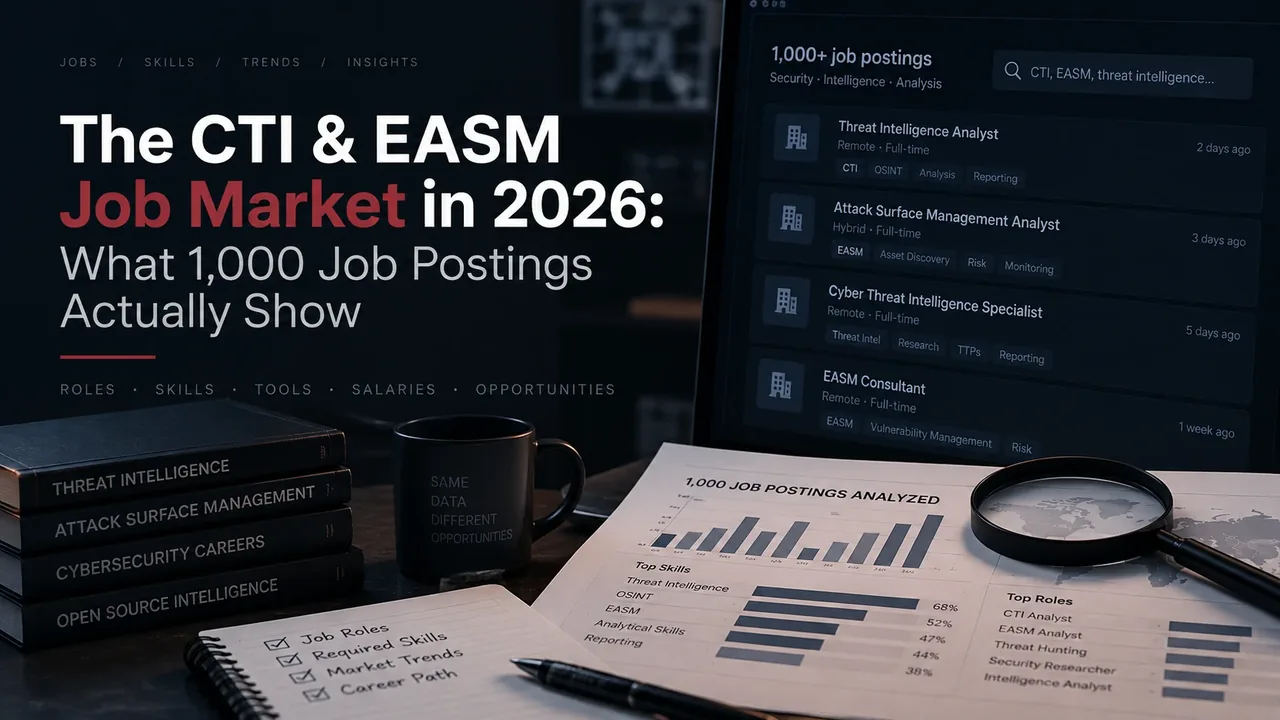
The CTI & EASM Job Market in 2026: What 1,000 Job Postings Actually Show
We scanned 1,000 cybersecurity job postings and went deep on 214 CTI and 54 EASM listings to find out what employers actually ask for. Here's the skill data, the salary ranges, and what it means for anyone deciding where to start.
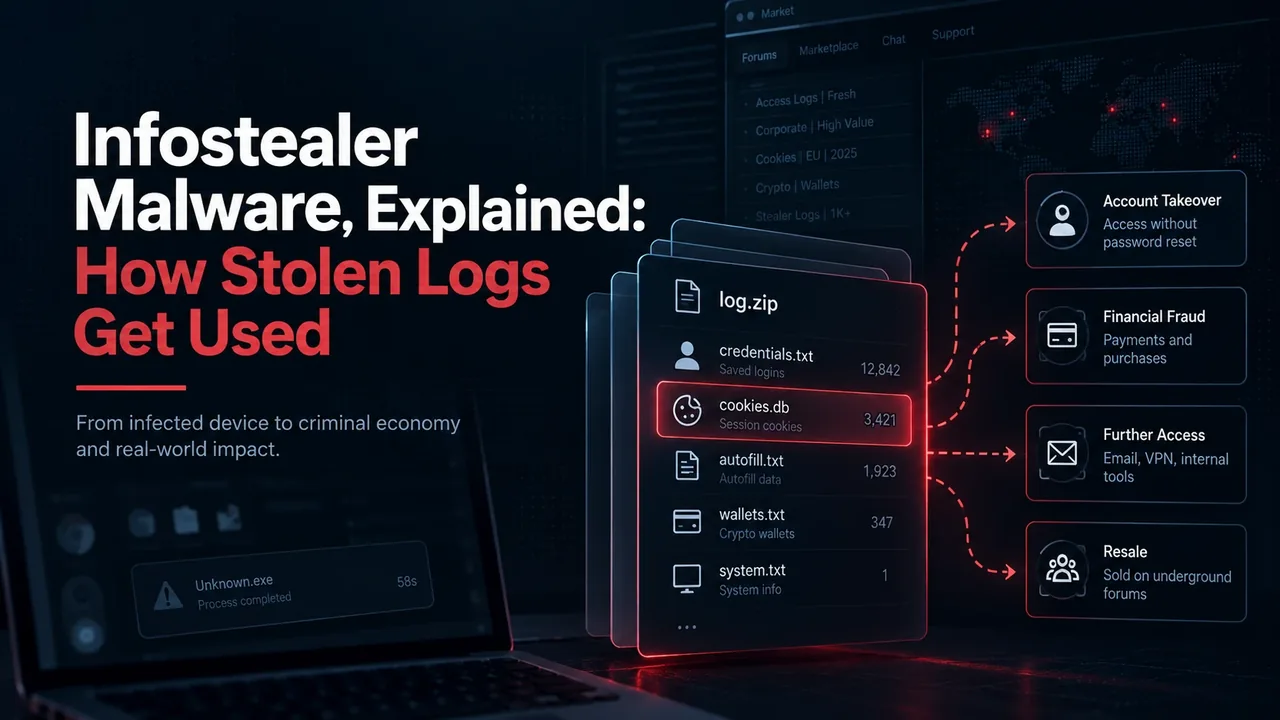
Infostealer Malware, Explained: How Stolen Logs Get Used
An infostealer does not break anything, it runs once, copies what the browser already remembered, and leaves. The file it produces, a stealer log, is worth more to the criminal economy than the access it had. How the chain works, why the Lumma takedown didn't hold, and why a password reset is not enough.
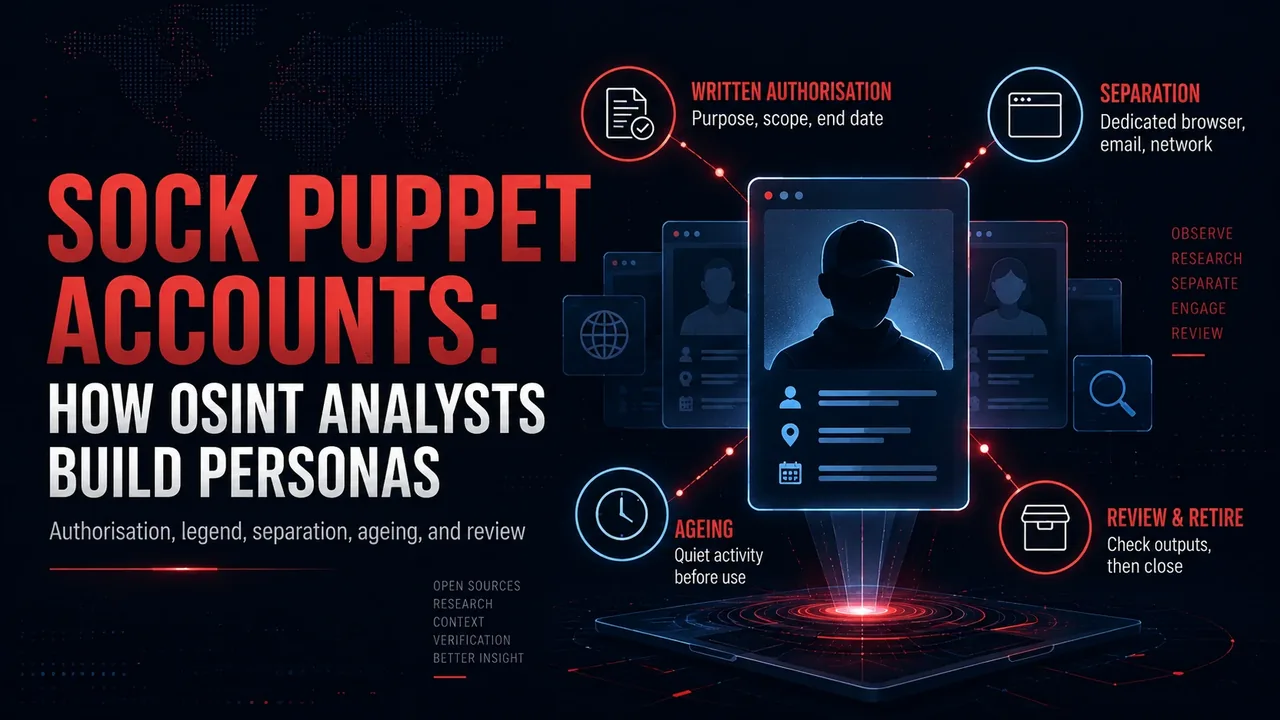
Sock Puppet Accounts: How OSINT Analysts Build Personas
Most research accounts are not burned by clever adversaries, they are burned by the analyst who made them, and by the account nobody ever authorised in writing. This is a working method for building an OSINT research persona: the six-step process, the law behind it, and how platform detection has evolved.
Living Off the Land: Why Attackers Prefer Your Own Windows Tools
There is no malware in a living off the land intrusion. No implant, no dropper, no new file for antivirus to recognise. The intruder signs in with a working password and runs the same programs your administrators run all day, every one written and signed by Microsoft, and on the disk long before anyone attacked anything. CrowdStrike counted 82 percent of its detections in 2025 as malware-free, up from 51 percent in 2020.
Entry-Level CTI Jobs: Where to Find Them and How to Land One
Ninety percent of organizations now have dedicated threat intelligence resources, and most of those teams run on four or fewer analysts. That gap between demand and headcount is why entry-level threat intelligence jobs exist almost everywhere but rarely carry the title you'd search for. This guide covers the seven employer categories that actually hire juniors, the job titles that hide CTI work, and what gets an application shortlisted instead of filtered.
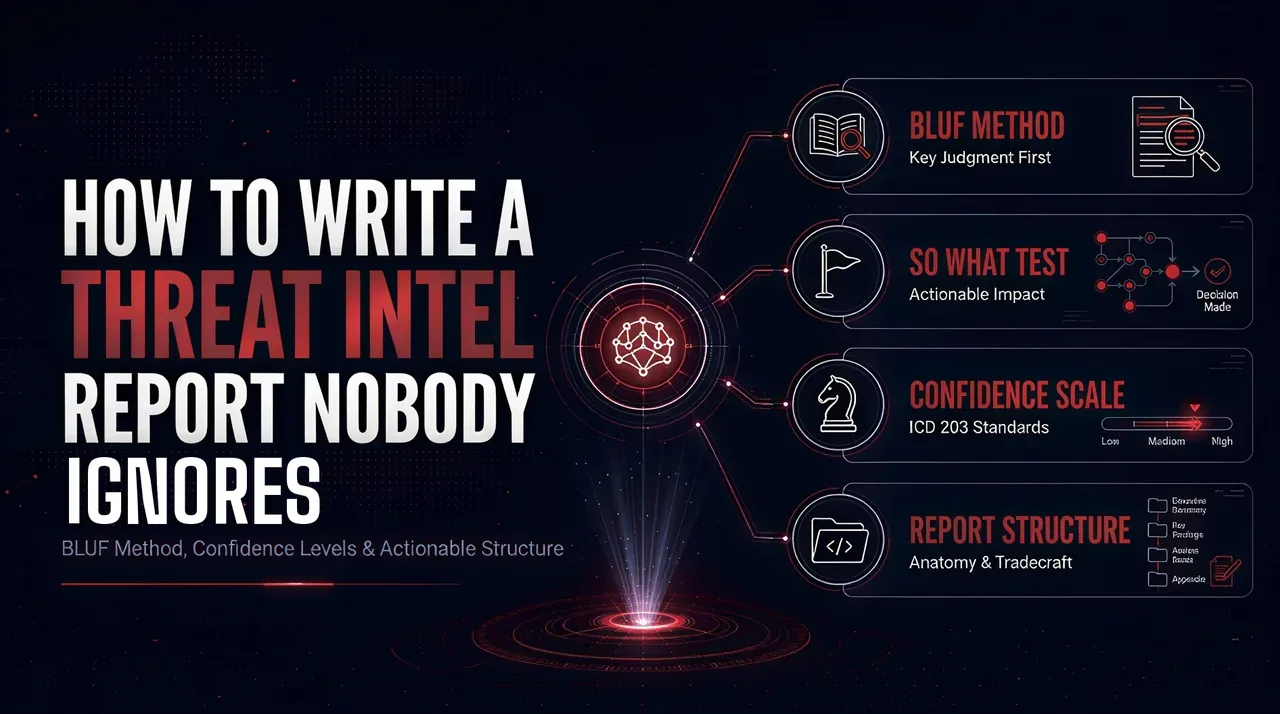
How to Write a Threat Intel Report Nobody Ignores
How to write a threat intelligence report people actually act on: the BLUF method, the so-what test, standardized probability and confidence language, and the seven-part structure that survives a busy reader. Includes the ICD 203 rule almost nobody follows about never mixing confidence and likelihood in the same sentence.
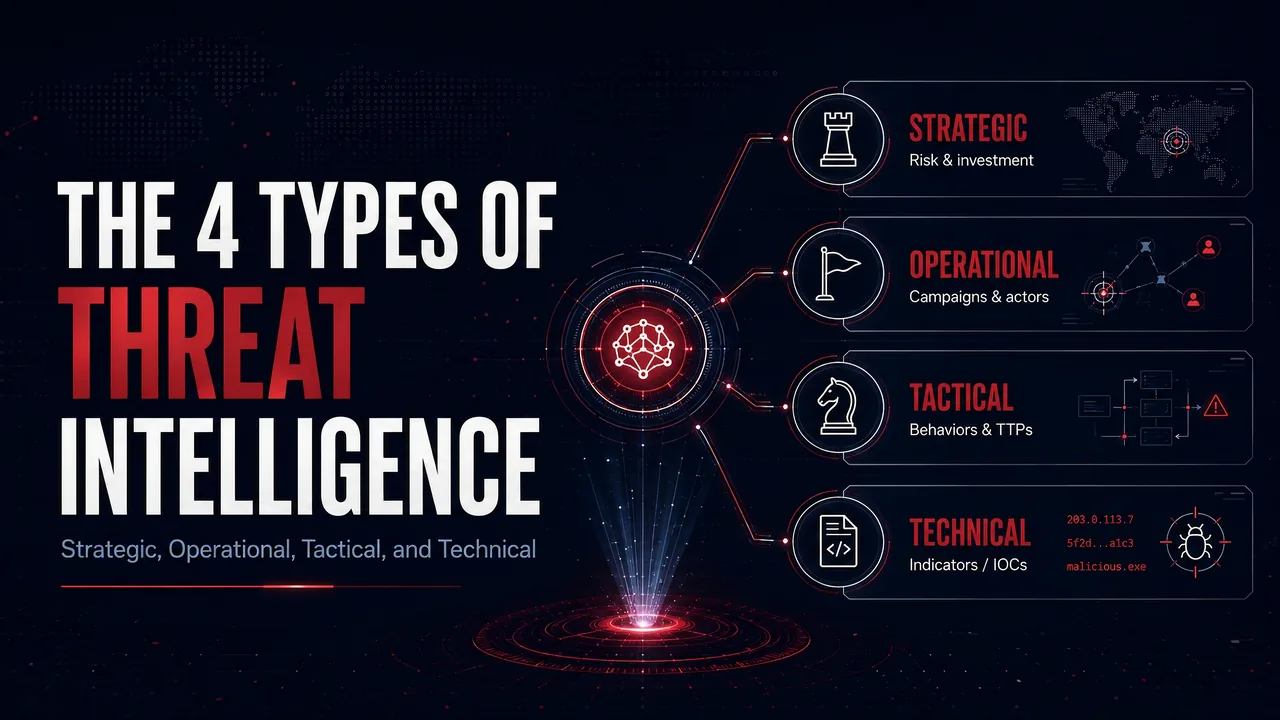
The 4 Types of Threat Intelligence, Explained
Threat intelligence comes in four types: strategic, operational, tactical, and technical. Learn what each one is, who reads it, how long it stays useful, and see real 2025 examples from Scattered Spider's campaigns and Verizon's DBIR data.
Bulletproof Hosting and the Money Mule Ecosystem, Explained
One bulletproof hosting provider sanctioned in late 2025 had been serving attackers since 2015, outlasting nearly every ransomware gang that rented from it. This guide breaks down the two support layers that keep cybercrime running: bulletproof hosting infrastructure and the money mule networks that launder the proceeds, plus the 2025-2026 sanctions crackdown and what it means for CTI analysts.
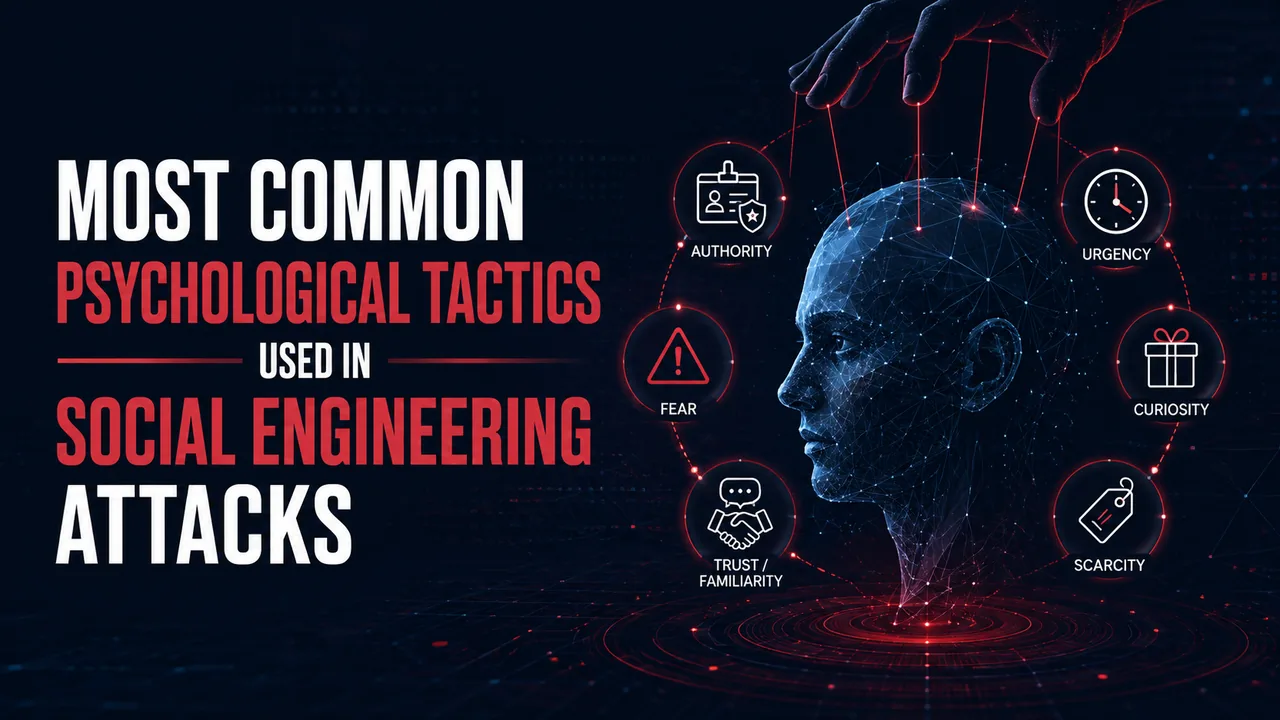
Most Common Psychological Tactics Used in Social Engineering Attacks
In 2025, a threat group went from a single help-desk phone call to full domain administrator access in about forty minutes, without using any malware. This is what social engineering psychological tactics actually look like: authority, urgency, fear, and helpfulness, stacked together and aimed at the mental shortcuts that make normal professional life possible. Here is how each lever works, why training alone doesn't stop them, and the defenses that hold up under pressure.
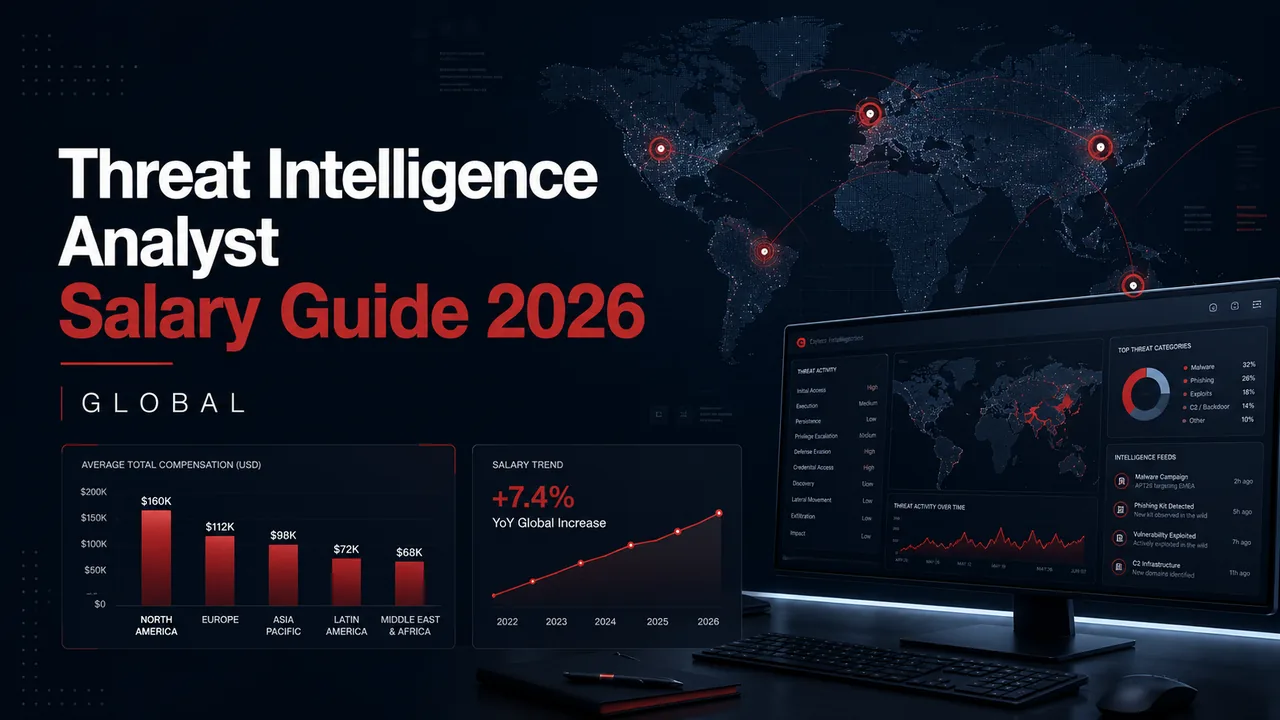
Threat Intelligence Analyst Salary Guide 2026 (Global)
A global 2026 salary guide for threat intelligence analysts: real US, UK, Europe, India, UAE, Singapore, and Australia pay ranges, why the numbers disagree so wildly, and the factors, from seniority to security clearance, that actually move your pay.
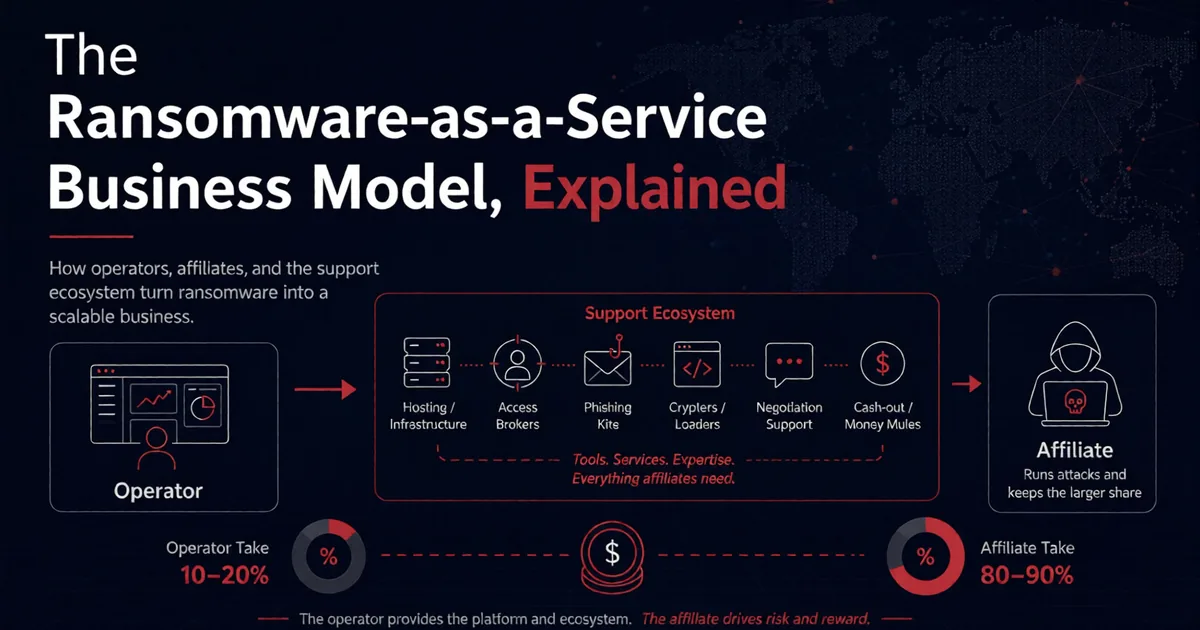
The Ransomware-as-a-Service Business Model, Explained
How the RaaS business model actually works in 2026: the operator/affiliate revenue split, why power has shifted to affiliates, why brand takedowns like LockBit and RansomHub didn't shrink the market, and the rise of encryptionless extortion.
SOC Analyst vs CTI Analyst: Which Cybersecurity Career Fits You?
Ask ten CISOs where they started, and eight will say some version of a security operations center. SOC analyst and CTI analyst are not a fork in the road, they are two seats on the same team, and one is the most common on-ramp to the other. Here is the honest comparison: salary, mindset, burnout, and the career path between the two roles.
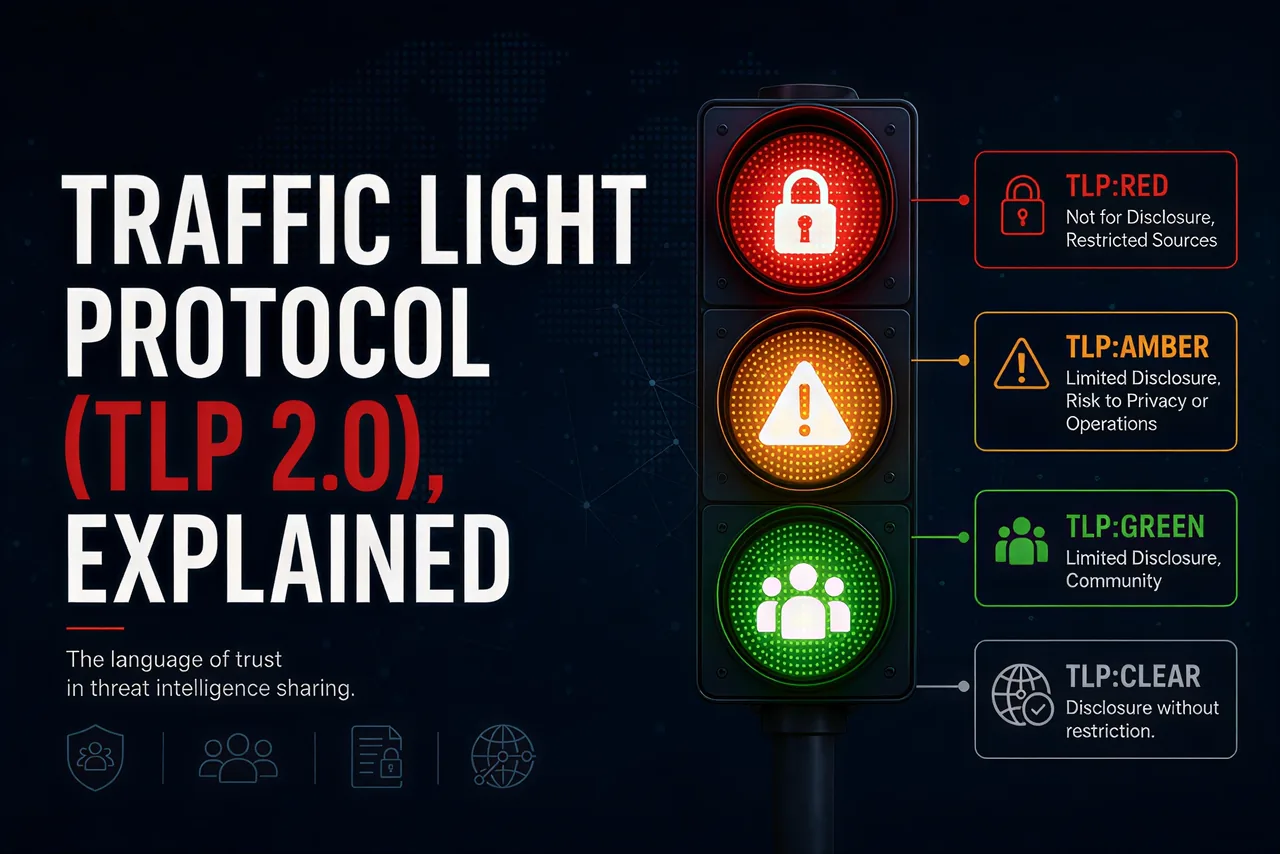
Traffic Light Protocol (TLP 2.0), Explained
The fastest way to get quietly cut out of an information sharing community is not leaking something. It is mislabeling it. The Traffic Light Protocol exists to prevent exactly that: four short labels, standardized as TLP 2.0 by FIRST, that tell a recipient how far they may pass something on.
Best Threat Intelligence Books, Ranked by a Practitioner
The threat intelligence books that actually matter in 2026: the CTI core every analyst should read first, the desk references for structured analysis and program-building, the underground classics on cybercrime and dark web tradecraft, and the narrative nonfiction that builds judgment over time.
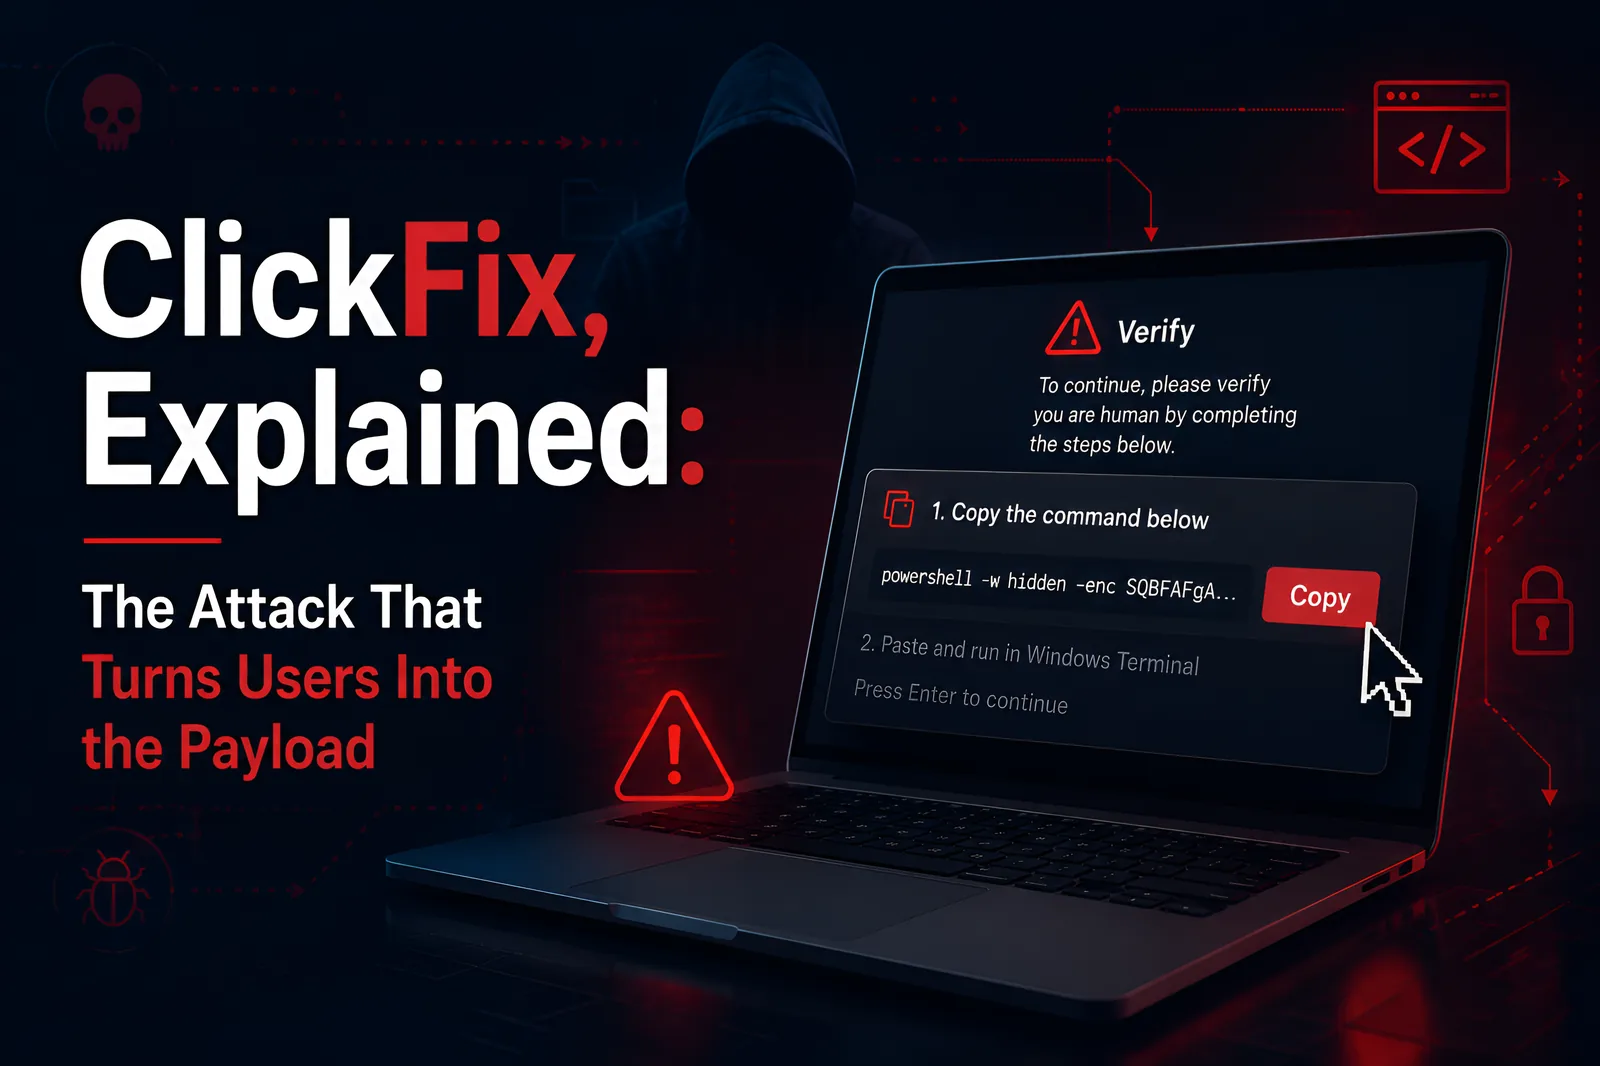
ClickFix, Explained: The Attack That Turns Users Into the Payload
There is no exploit in a ClickFix attack. The victim runs the malware themselves, copying a command off a fake CAPTCHA or update page and pasting it into their own machine. In 2025, Microsoft attributed 47% of all initial access intrusions it tracked to this one technique. This guide breaks down how ClickFix works, dissects three real campaigns, and covers exactly how to detect and defend against it.
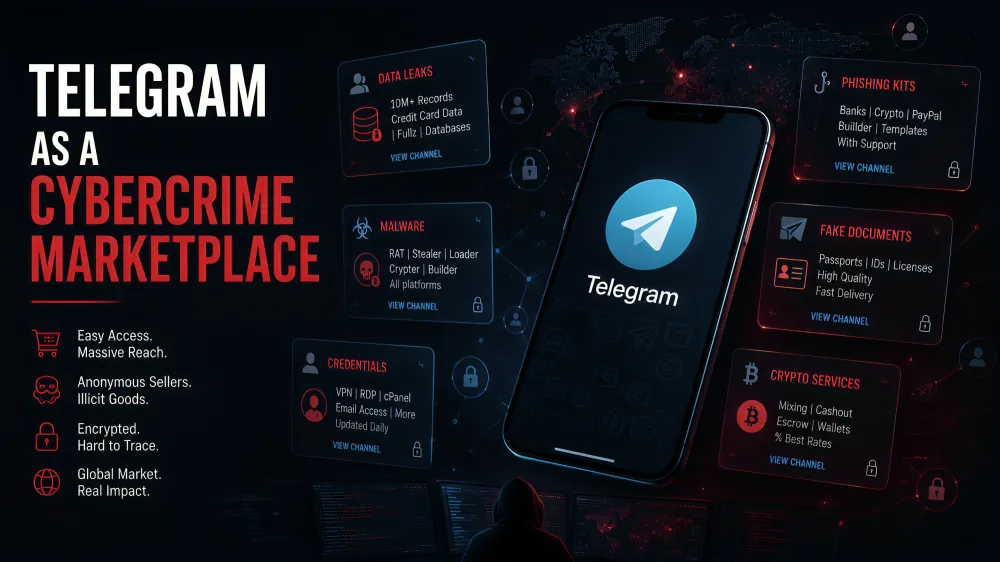
Telegram as a Cybercrime Marketplace
Telegram is not the dark web, but its communication, marketplace, automation, and amplification layers have turned it into one of cybercrime's busiest storefronts. See what gets sold, how OTP bots and log-search bots automate the trade, why the 2025 Durov-era crackdown didn't empty the shelves, and how CTI analysts monitor it for early warning.
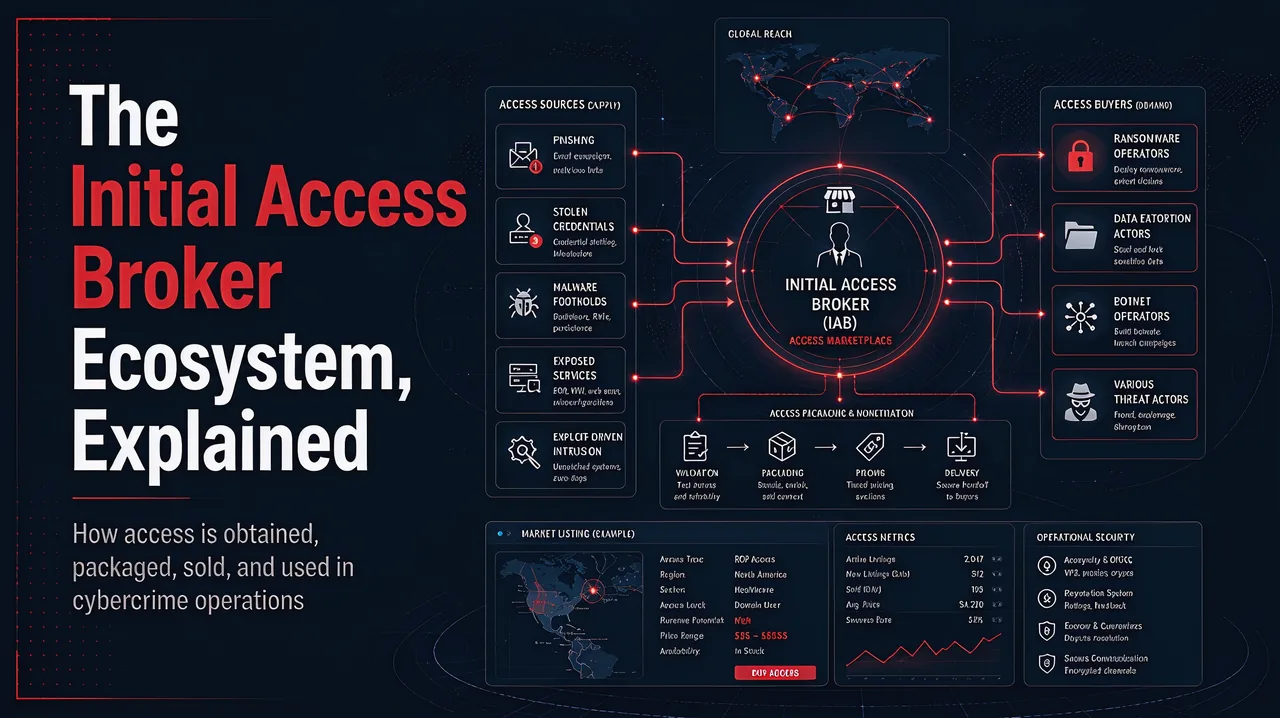
The Initial Access Broker Ecosystem, Explained
How the initial access broker economy actually works: the supply chain from infostealer logs to ransomware deployment, what access costs in 2026, where the market lives, and how CTI analysts track it as an early-warning signal.
How to Become a CTI Analyst in 2026
A practitioner's roadmap to becoming a cyber threat intelligence analyst in 2026: what the job actually involves, realistic salary ranges, whether you need a degree, the skills that matter, and the exact order to earn certifications like Security+, CTIA, and GCTI.
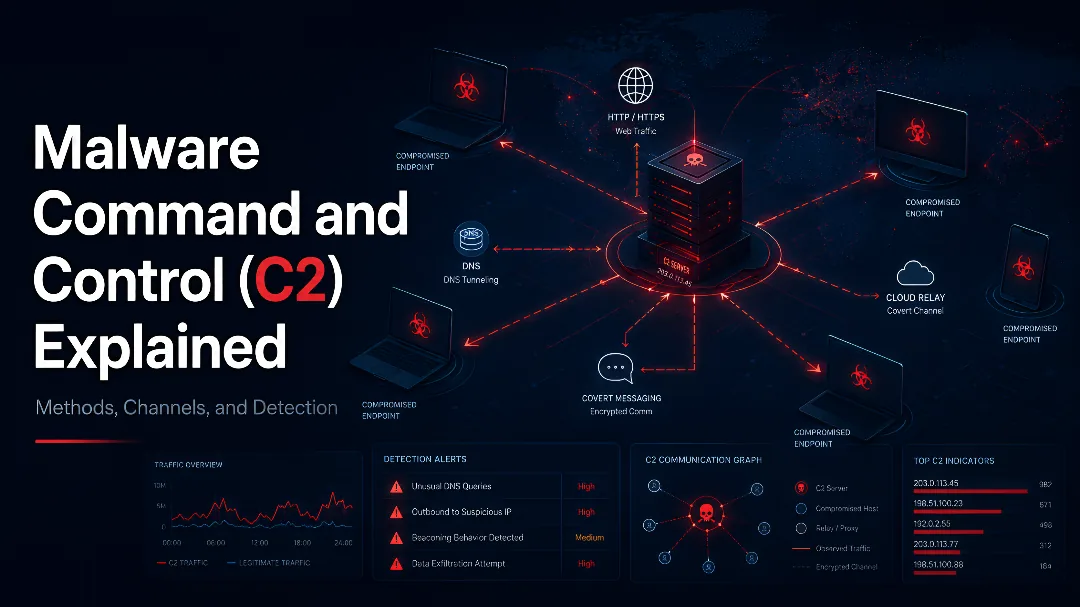
Malware Command and Control (C2) Explained
Command and control (C2) is the communication channel a threat actor uses to remotely operate compromised systems. This guide breaks down how every major C2 method works, from HTTP beaconing and DNS tunneling to domain fronting, trusted-service abuse, and blockchain-based channels, along with the logic behind each technique and how defenders detect C2 traffic.
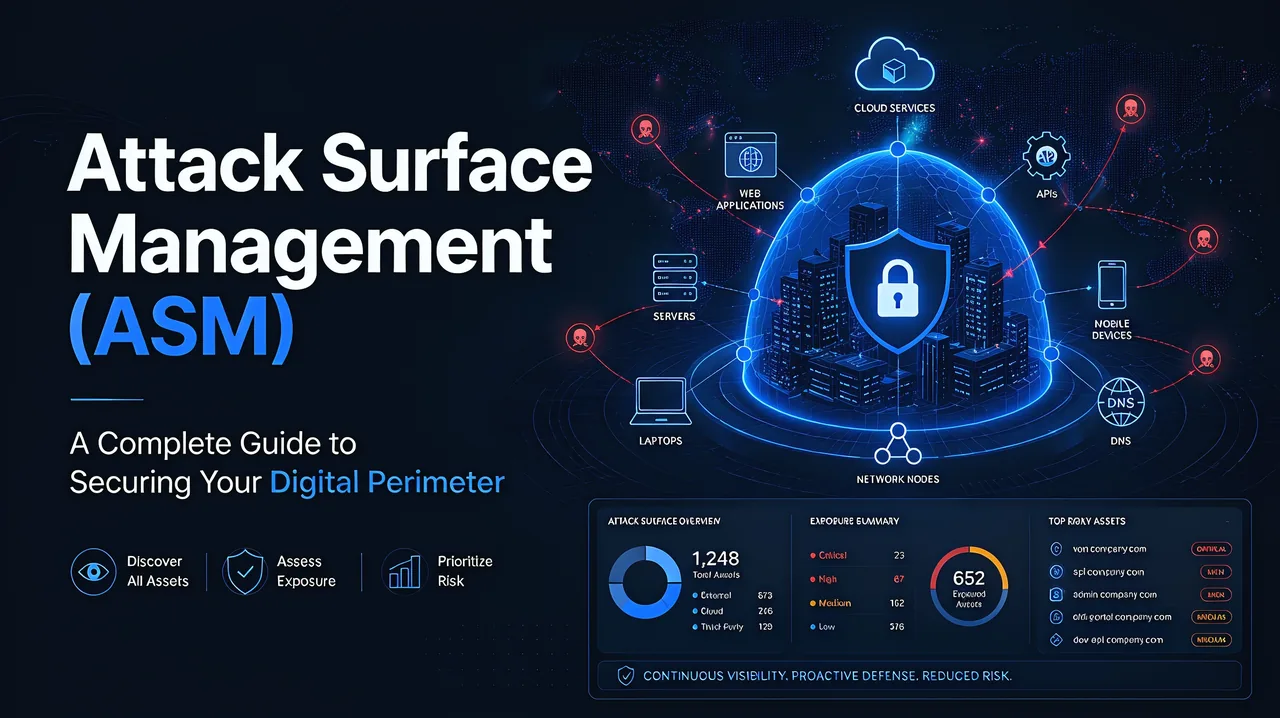
Attack Surface Management (ASM) Guide
Attack Surface Management (ASM) is the continuous process of discovering, cataloging, and securing all internet-facing assets that an attacker could target. Unlike traditional vulnerability management that focuses on known assets, ASM starts from the attacker's perspective, identifying assets your organization may not even realize are exposed.
What Is Cyber Threat Intelligence (CTI)?
Every day, organizations face thousands of cyber attacks ranging from automated phishing campaigns to sophisticated nation-state intrusions. The sheer volume and complexity of these threats make it impossible to respond reactively. This is where Cyber Threat Intelligence (CTI) comes in -- it transforms raw data about threats into actionable knowledge that defenders can use to anticipate, prevent, and respond to attacks before they cause damage.
OSINT: The Complete Guide
Open Source Intelligence (OSINT) is the practice of collecting, analyzing, and acting on information gathered from publicly available sources. In a world where digital footprints expand with every click, OSINT has become one of the most powerful disciplines in cyber threat intelligence, law enforcement, journalism, and corporate security. Whether you are investigating a phishing campaign, verifying a source, or mapping an organization's attack surface, OSINT provides the foundation for evidence-
Linux for Cyber Threat Analysis
When a security incident strikes, the analysts who respond fastest are almost always the ones working from a Linux terminal. No GUI overhead, no waiting for tools to load -- just raw, scriptable power at your fingertips. Whether you are investigating a compromised server, hunting for indicators of compromise (IOCs) across terabytes of logs, or performing memory forensics on a suspected rootkit, Linux gives you the flexibility and depth that no other platform can match.
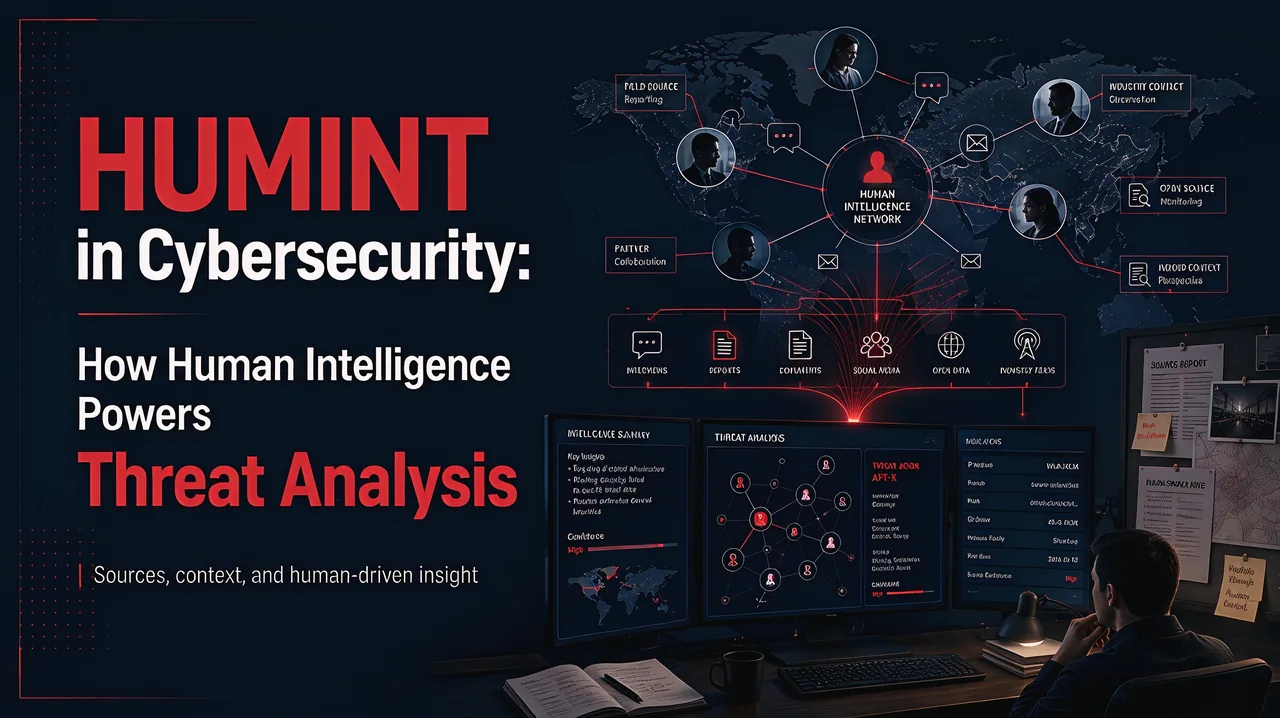
What Is HUMINT in Cybersecurity?
HUMINT, or Human Intelligence, is the collection of information through interpersonal contact and human sources. Unlike signals intercepts or satellite imagery, HUMINT relies on direct engagement between intelligence officers and individuals who possess valuable knowledge. It is the oldest form of intelligence gathering, stretching back thousands of years to the earliest recorded civilizations.
Introduction to Information Security
Every organization, from global enterprises to small startups, depends on digital infrastructure. With that dependence comes risk. Cyberattacks are growing in frequency, sophistication, and impact, making information security one of the most critical disciplines of the modern era. Whether you are a student exploring career options, an IT professional looking to pivot, or a business leader trying to understand the threat landscape, this guide will give you a solid foundation in the principles, pr